If you operate a website, you’re already aware that a single unpatched vulnerability can render your site inaccessible, compromise your reputation, or necessitate extensive remediation following an attack. Most security breaches we observe originate from automated attacks that exploit known software vulnerabilities, often the same ones that have…
Sucuri
Critical PHP Security Update: Two RCE Flaws (CVE-2026-109618, CVE-2026-109619)
Two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619) can allow unauthenticated attackers to execute code on affected web servers. Both carry a CVSS v4.0 score of 9.2, and exploitation attempts are already being observed in the wild. PHP has released the following fixed versions: PHP branch Fixed version PHP…
HTTP 401 Unauthorized: What It Means and How to Fix It
You load your site, or visit an API endpoint your app relies upon, and instead of a page you find a brief, unhelpful message: 401 Unauthorized. Sometimes a browser password box appears. Other times, a blank white page presents only that number. In either case, visitors are shut…
500 Internal Server Error: What It Means and How to Fix It
You load your own site, and instead of your homepage you get a blank page with a line of text reading 500 Internal Server Error. No explanation, no stack trace, nothing to act on. For visitors, it looks like the site is simply gone, and for you it…
What Is Encryption? How It Protects Your Website and Its Data
If you run a website, you’ ve already met encryption even if you’ ve never used the word. It’ s the 🔒 padlock in the browser bar, the reason your host told you to stop using plain FTP, and the checkbox on your backup settings that says “ encrypt archive.” Encryption is one…
Vulnerability & Patch Roundup — September 2026
If you operate a website, you’re already aware that a single unpatched vulnerability can render your site inaccessible, compromise your reputation, or necessitate extensive remediation following an attack. Most security breaches we observe originate from automated attacks that exploit known software vulnerabilities, often the same ones that have…
SC WordPress Malware: A Self-Healing Mesh of Loaders, Drop-Ins, and a Blockchain-Controlled Backdoor
Overview During recent website cleanup work, we analyzed a WordPress compromise where the same backdoor kept returning within seconds of every removal, no matter how carefully the visible files were deleted. Throughout this article, we’ ll refer to this family of malware as SC, named after the “SC_” markers…
WordPress Security Plugins: How to Choose the Right One
In short, WordPress security plugins are tools you add to your site to strengthen your settings, scan for malware, watch for file changes, and block suspicious activity from within WordPress. Most sites should use one, along with a firewall that filters traffic before WordPress even loads. Look for…
Vulnerability & Patch Roundup — August 2026
If you operate a website, you’re already aware that a single unpatched vulnerability can render your site inaccessible, compromise your reputation, or necessitate extensive remediation following an attack. Most security breaches we observe originate from automated attacks that exploit known software vulnerabilities, often the same ones that have…
Third-Party Script Security: How Tags, Pixels, and Embeds Can Put Websites at Risk
Third-party scripts are common on websites. They help with analytics, ads, live chat, social media, video, payments, and many other features. While not all are risky, every external tag, pixel, widget, or embed adds to your website’s vulnerability. These tools can read page content, collect visitor data, change…
What Is a Website Attack Surface? A Beginner’s Guide to Reducing Risk
Each feature that you add to a website results in a new element that has to be managed. The credentials are accepted by a login page, the data by a contact form, new code is introduced by a plugin, and an API is used to connect your website…
The Illusion of a Lock – How AI is changing the speed and scale of hands-on WordPress vulnerability research.

2026: the year the tools learned to hack In May 2026, OpenAI began testing an internal research model against a cybersecurity benchmark called ExploitGym. While the test environment was not supposed to have access to the open internet, there was, however, one narrow path out because the agents…
How to Create a Secure WordPress Staging Site: Beginner’s Guide

Updating WordPress directly on a live website can cause avoidable problems. A plugin update might break checkout, or a theme change could create layout issues visitors see immediately. A WordPress staging site gives you a separate place to test changes before they reach your live website. Staging reduces…
Upgrading How You Sign In to Your Sucuri Account

Starting August 10, 2026, Sucuri will begin moving customer account logins to a new authentication platform designed to provide a stronger, more modern sign-in experience. The rollout will happen gradually over the following few weeks, so not every account will transition at the same time. For most users, …
Vulnerability & Patch Roundup — July 2026

Running a website means a single unpatched vulnerability can take it offline, harm your reputation, or require cleanup. Most compromises begin with automated attacks exploiting known software flaws, usually reported and disclosed already. To keep you protected from these threats, we’ve compiled this month’s key security updates and…
Why Delaying WordPress Updates Increases Security Risks

WordPress updates help close known vulnerabilities before automated attacks can find and exploit them. Once a patch is released, attackers often move quickly to scan for sites that have not yet updated. It’s easy to put off updates when everything seems to be working. But once a vulnerability…
Vulnerability & Patch Roundup — June 2026
Running a website means a single unpatched vulnerability can take it offline, harm your reputation, or require cleanup. Most compromises begin with automated attacks exploiting known software flaws, usually reported and disclosed already. To keep you protected from these threats, we’ve compiled this month’s key security updates and…
PCI Compliance Isn’t a Checkbox: How to Secure Ecommerce Checkouts Before Attackers Arrive
A working checkout page is often the moment a business starts to feel real. The products are live, the cart is functional, payments are flowing, and orders are landing in your inbox. That is also when security shifts from a background concern to a real-world risk. Once your…
WordPress PBN Plugin Drops Dual Webshells via Database Injection
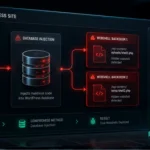
During a recent incident response engagement, our team uncovered a multi-stage WordPress infection that goes beyond the usual file-based malware. The attacker combined a fake plugin, a remote command-and-control server, and two PHP web shells stored directly inside the WordPress database. The campaign is operated by a Turkish-speaking…
Vulnerability & Patch Roundup — May 2026
If you run a website, you know that a single unpatched vulnerability can take your site offline, damage your reputation, or leave you cleaning up after an attack. Most compromises we see start with automated attacks targeting known software flaws, often the same ones that have already been…
